PrivateAI-Platform Add-on
Core-Pilot Knowledge
Reduce the risk of leaking sensitive data such as executive compensation. Control who can reach which information with role-based access, and use AI across the company with greater confidence.
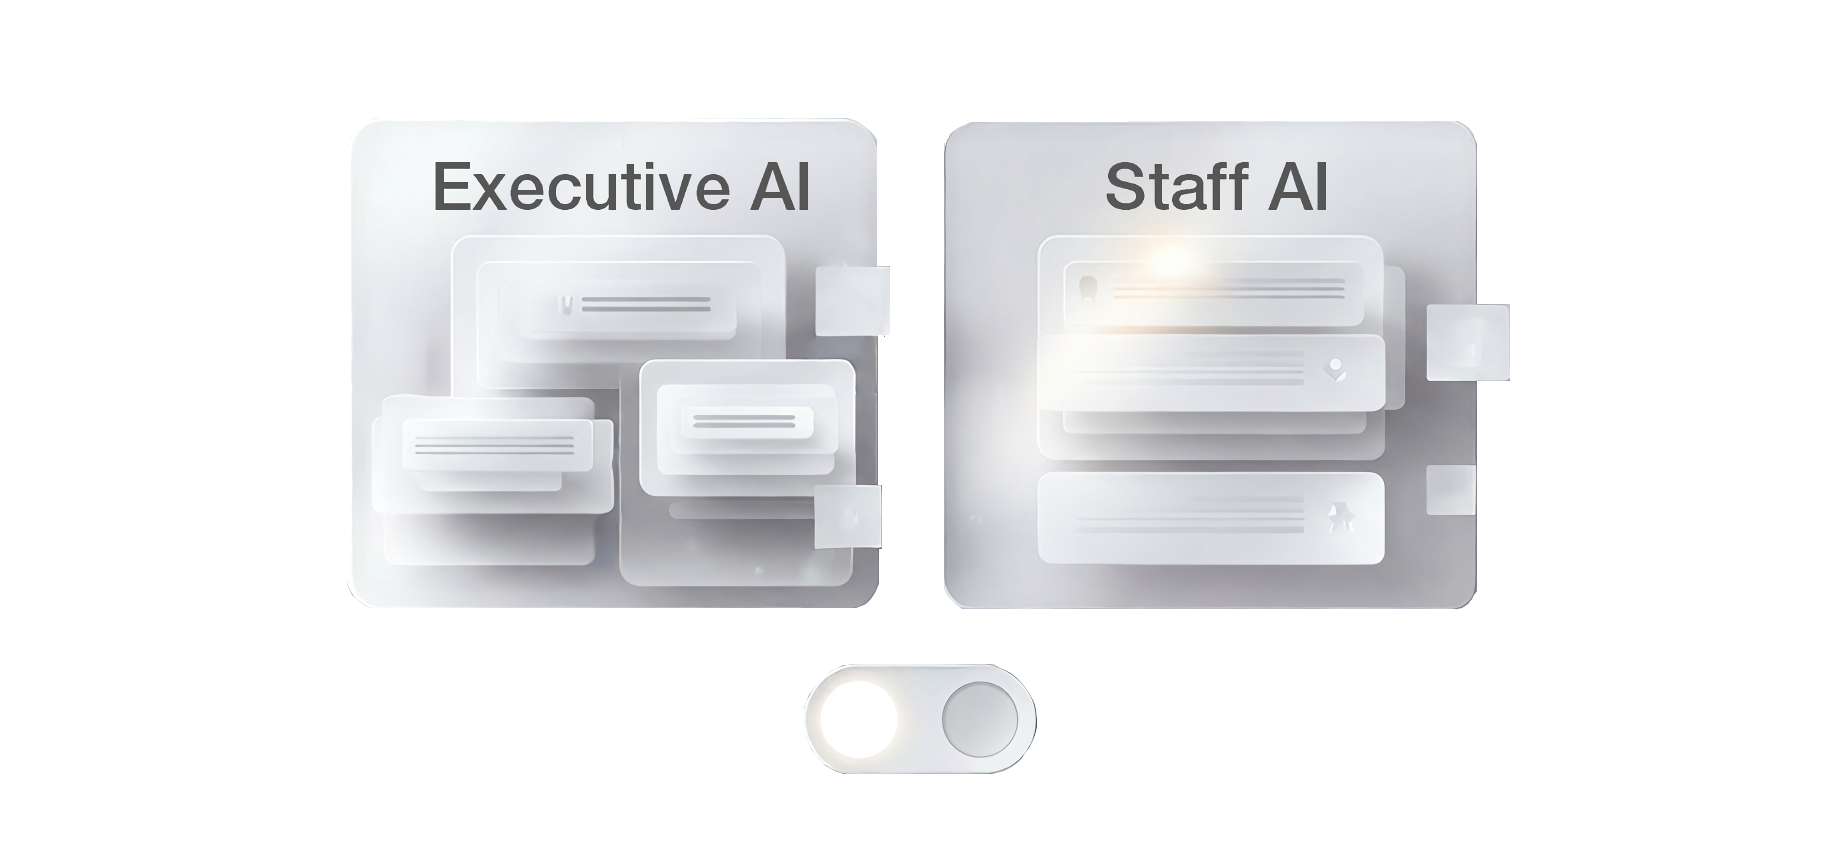
Addressing the "Over-Exposure" Risk in Company-wide AI Deployment
-
01 Efficiency
Less Document Management OverheadTraditional methods, such as manually assigning metadata-based permissions to every single file, often break down when the organization changes. Our approach reduces this burden by isolating applications by role. Simply upload your files to the designated workspace. We provide a secure RAG environment that leverages Dify's capabilities without the operational overhead.
-
02 Security
Separation at the Application LevelWe generate role-specific applications, so access is separated right at the entry point. Instead of relying on the AI's "judgment" to filter responses, we structurally control the underlying data sources. This design reduces the risk of data leakage through prompt injection and supports strict data governance within your dedicated AWS environment.
Using AI with confidential data
across your organization.
This feature can be added as an add-on after the initial platform implementation. Please tell us about your organization and the data you want to protect.
Contact Us